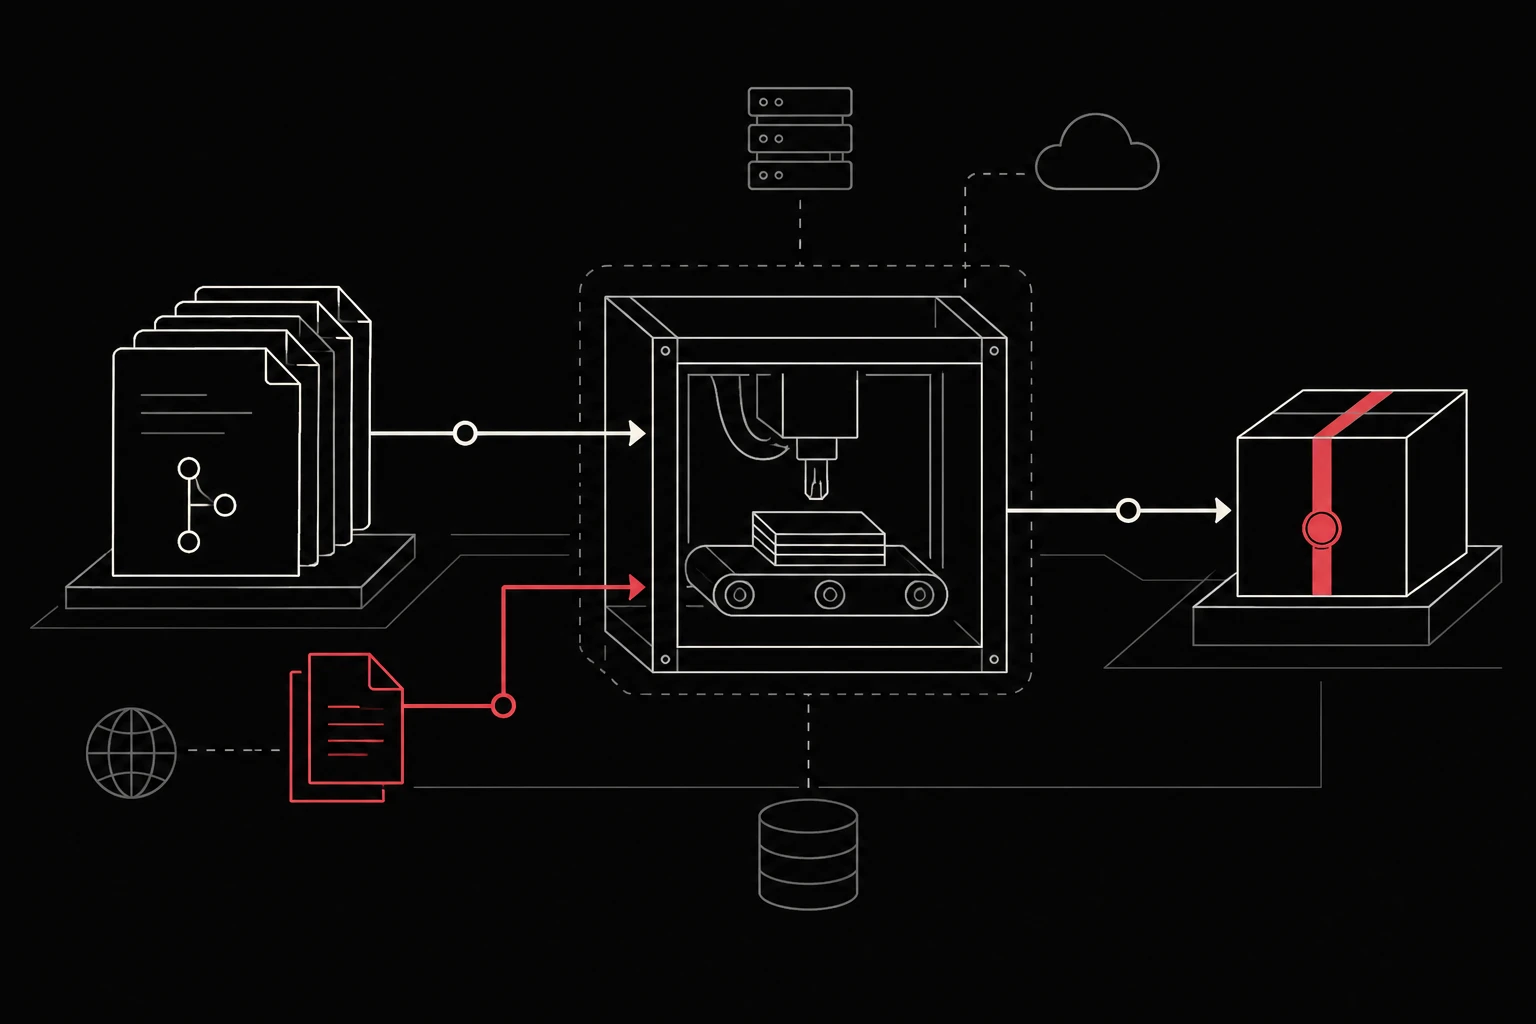
Follow the delivery chain from workflow trigger to untrusted input, token permissions and the produced artifact. A dependency update can change installation behavior at the same time that a workflow gives it access to credentials or release permissions.
01 / Gather the change and the build context
Gather the before-and-after lockfiles, workflow definition and intended registry policy. Identify the triggering event, the input it brings into the job and the permissions available at each step.
Use the public dependency and workflow tools to compare the supplied metadata and configuration. Review the actual package contents and build context separately when the question concerns executed behavior.
02 / Follow the changes across trust boundaries
Inspect changed package sources, integrity fields and recorded installation hooks. Trace issue text, pull-request context or other external input through workflow steps and helper actions.
Which step first gains a privileged token? Are the referenced actions pinned as intended? Can the same untrusted input influence the artifact later published by a more privileged job? Resolve those questions against the actual workflow.
03 / Keep the inputs and the reasoning together
Keep the compared inputs and review output with the relevant workflow step. Record the source of the input, the permissions it reaches and the artifact or configuration affected.
Distinguish a metadata change that needs approval from a confirmed unsafe path. Explain which additional package or build evidence resolves the question.
04 / Recheck the changed inputs and effective configuration
Recheck the changed dependency or workflow configuration. Confirm the effective permissions and installation source in the intended build, and compare the artifact path that motivated the review.
Regenerate lockfiles from reviewed inputs rather than editing metadata to clear a result. Verify installation and build compatibility in the authorised environment.
Questions to resolve before the review
- Which artifact and installation source will the build consume?
- Can an untrusted input affect a privileged workflow step?
- Which checks were repeated, and which runtime conditions still need verification?